


August Risk Roundup: Hack a company, get a job
Was it a clever ploy for notoriety? While their motivations remain unclear, one of the hackers who stole and returned hundreds of millions in cryptocurrencies received a job offer from their victim. Read on for our thoughts on this calculated development and other ways to keep your company and personal data safe.
1. Hacker who stole and gave back $600M offered job, reward
Depending on the laws in play, this may all be a ruse to reveal Mr. White Hat's identity for prosecution. Even if the company doesn’t want to prosecute, they may not have the final say, and law enforcement may intervene. – Scott Walsh, Senior Engineer
2. 'Unique' phishing attack uses Morse code
Sometimes hiding in plain sight is easy — the more normal your communications look, the harder it can be to detect if they’re malicious. Morse code is well established but not widely used; the encoded information is in plain sight but can be easily overlooked because defenders aren’t looking for something that was popular last century. Security is like pinball; you can never win, you only keep playing. – Scott Walsh, Senior Engineer
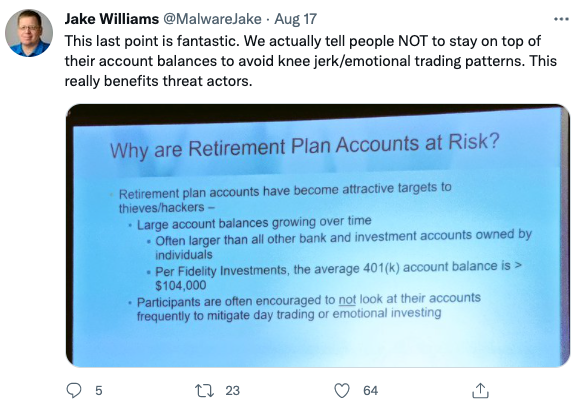
3. Why are retirement plan accounts at risk
Very few things are more critical to an individual than protecting their families’ retirement. Unfortunately, retirement accounts are a massive target for bad actors. Utilizing a password manager to keep your passwords unique and secure and enabling two-factor authentication (not via text!) to access your accounts is an extremely easy, low-cost way to protect your future. – Ross Warren, Production Underwriter
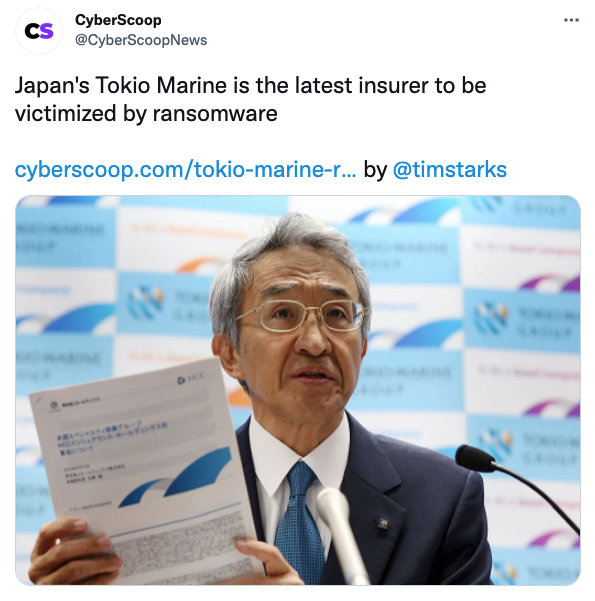
4. Japan's Tokio Marine victimized by ransomware
All industries, even large insurance companies that provide cyber insurance coverage, are vulnerable to ransomware attacks. And it’s only going to get worse. In order to step up defenses, companies should focus on training employees to be vigilant, enable MFA, segment data, test backups often, and ensure role-based network access and service level restriction. – Kirsten Mickelson, Claims Counsel
If you enjoyed this post be sure to check our blog weekly; the Risk Roundup runs Friday mornings in addition to more enlightening content we post related to the ever-evolving landscape of digital risk. Follow us on Twitter (@SolveCyberRisk) and LinkedIn (Coalition Inc). If you have any suggestions for content that we should be adding to our reading list, let us know!
Related blog posts

Blog
Why PHP2Shell Claims Will Lag Exploits by Weeks
Cyber insurance claims from PHP2Shell haven’t arrived en masse yet. Did we overhype the PHP vulnerabilities or is this the calm before the storm?


Blog
Security Alert: Critical PHP Vulnerabilities Put Most of the Web at Risk
Coalition is actively urging all businesses using PHP to patch two critical vulnerabilities in software widely used across the internet.

Blog
Designing Security for the People Who Have to Live With It
Anyone who tells you security doesn't introduce friction is lying. Protection comes at a cost, and it’s usually paid in someone else's time and attention.
