


July Risk Roundup: Cybersecurity shiny objects — don’t overlook the basics
A healthy dose of skepticism is never a bad idea in cybersecurity. People will try to take advantage of chaotic situations, bad ideas will be expressed when people have ulterior motives, and sometimes a flashy headline is designed to sell you ads rather than give you useful information.
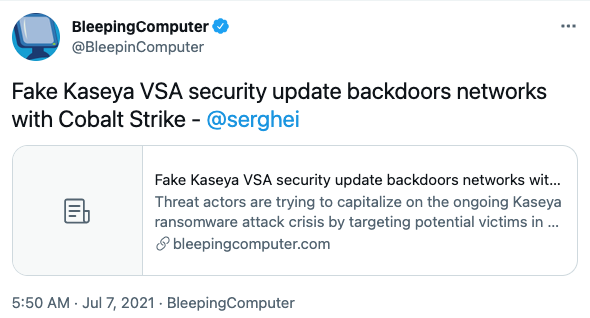
1. Fake Kaseya VSA security update backdoors networks with Cobalt Strike
Attacker’s creed: never let a good disaster go to waste. The lesson for defenders? Chaotic conditions demand extra vigilance – when things go wrong, it’s helpful to have defined procedures and team members trained via exercises/drills to respond.
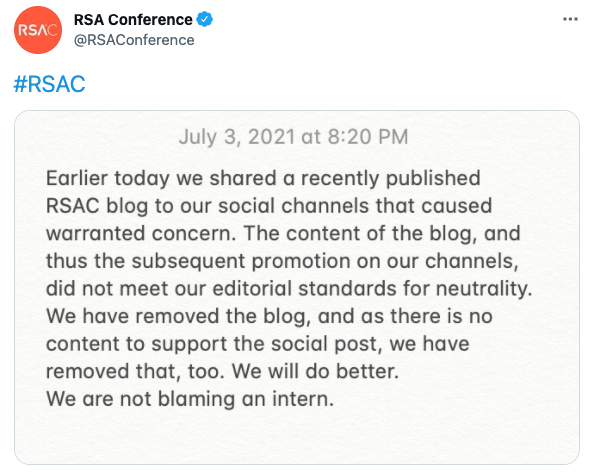
2. RSA sponsored content issues
Kudos to RSA for (retroactively) policing their sponsored content and dunking on the “blame the interns” meme. But how did an article about blockchain fixing TCP/IP security issues that didn’t demonstrate a solution at all make it through editorial reviews?
3. Headline-driven threat landscape
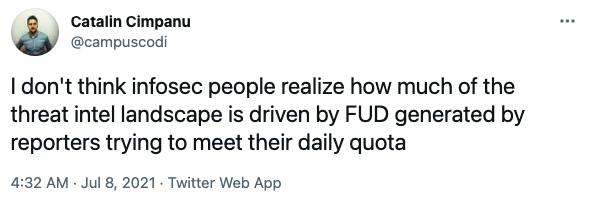
Media sensationalism is nothing new, and the problem is worse in tech and infosec due to unfamiliar vocabulary. It takes time and effort to contextualize cyber risk, so both infosec and business leaders need to allocate that time rather than following clickbait headlines.
If you enjoyed this post be sure to check our blog weekly; the Risk Roundup runs Friday mornings in addition to more enlightening content we post related to the ever-evolving landscape of digital risk. Follow us on Twitter (@SolveCyberRisk) and LinkedIn (Coalition Inc). If you have any suggestions for content that we should be adding to our reading list, let us know!
Related blog posts

Blog
Inbox In-Fighting: A Window Into BEC Subculture
Coalition Incident Response has observed threat actors using the names of inbox rules to communicate. What did we learn from hidden chats?

Blog
AI SOC Hype is Overdue for a Reality Check
There’s a massive difference between a tool that uses AI as a marketing veneer and a production-grade AI SOC built on real security engineering.

Blog
MSPs Report Losing Clients Over Slow Threat Containment
New study reveals 53% of MSPs lost a client in the past 24 months because they were unable to contain an incident fast enough.
